
Top Related Projects

Fast web fuzzer written in Go

Directory/File, DNS and VHost busting tool written in Go

httpx is a fast and multi-purpose HTTP toolkit that allows running multiple probes using the retryablehttp library.
Find domains and subdomains related to a given domain
Nuclei is a fast, customizable vulnerability scanner powered by the global security community and built on a simple YAML-based DSL, enabling collaboration to tackle trending vulnerabilities on the internet. It helps you find vulnerabilities in your applications, APIs, networks, DNS, and cloud configurations.

SecLists is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place. List types include usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and many more.
Quick Overview
dirsearch is a powerful web path scanner designed to brute force directories and files in websites. It's an advanced command-line tool written in Python that helps security researchers and penetration testers discover hidden content and potential vulnerabilities in web applications.
Pros
- Highly customizable with numerous options for fine-tuning scans
- Supports multiple wordlists and has a large default wordlist
- Can handle multiple targets simultaneously
- Includes features like recursive scanning, custom headers, and proxy support
Cons
- Can be resource-intensive for large scans or multiple targets
- Might trigger security alarms or be blocked by web application firewalls
- Requires careful use to avoid unintended impact on target systems
- Learning curve for advanced features and options
Getting Started
-
Clone the repository:
git clone https://github.com/maurosoria/dirsearch.git -
Install requirements:
cd dirsearch pip3 install -r requirements.txt -
Run a basic scan:
python3 dirsearch.py -u https://target.com -e php,html,js
This command scans https://target.com for directories and files with .php, .html, and .js extensions using the default wordlist. For more advanced usage, refer to the project's documentation.
Competitor Comparisons
Fast web fuzzer written in Go
Pros of ffuf
- Written in Go, offering better performance and cross-platform compatibility
- Supports multiple HTTP methods and custom headers
- Highly customizable with extensive filtering options
Cons of ffuf
- Steeper learning curve due to more complex command-line options
- Less built-in wordlists compared to dirsearch
Code Comparison
ffuf:
matcher := ffuf.NewMatcher(options.Matchers, options.Filters, options.MatcherMode)
runner := ffuf.NewRunner(conf, matcher)
err := runner.Run()
dirsearch:
def start(self):
    self.setup()
    self.force_exit = False
    self.recursive_bruteforce()
Key Differences
- Language: ffuf is written in Go, while dirsearch is in Python
- Performance: ffuf generally offers better speed and resource utilization
- Flexibility: ffuf provides more customization options, while dirsearch is simpler to use
- Wordlists: dirsearch includes more built-in wordlists
- Output: Both tools offer various output formats, but ffuf has more options
Use Cases
- ffuf: Ideal for advanced users requiring high performance and customization
- dirsearch: Better suited for beginners or those preferring a simpler, more straightforward tool
Directory/File, DNS and VHost busting tool written in Go
Pros of gobuster
- Written in Go, offering better performance and concurrency
- Supports multiple modes (DNS, vhost, directory bruteforcing)
- Actively maintained with regular updates
Cons of gobuster
- Less extensive wordlist options compared to dirsearch
- Fewer built-in features for output formatting and reporting
Code Comparison
dirsearch:
def recursive_scan(self, base_path):
    for word in self.dictionary:
        path = base_path + word
        if self.scan(path):
            self.recursive_scan(path + '/')
gobuster:
func (d *DNSExecutor) runDNS(word string) error {
    fqdn := fmt.Sprintf("%s.%s", word, d.domain)
    addrs, err := d.resolver.LookupHost(context.Background(), fqdn)
    if err != nil {
        return err
    }
    // Process results
}
Both tools offer directory and file bruteforcing capabilities, but their implementations differ. dirsearch is Python-based, providing flexibility and ease of customization, while gobuster leverages Go's performance benefits. gobuster's multi-mode functionality gives it an edge for versatility, but dirsearch offers more comprehensive wordlists and reporting features out of the box. The choice between them often depends on specific use cases and personal preferences.
httpx is a fast and multi-purpose HTTP toolkit that allows running multiple probes using the retryablehttp library.
Pros of httpx
- Faster performance due to concurrent processing and efficient Go implementation
- Broader functionality beyond directory enumeration, including probe, title extraction, and technology detection
- Supports multiple input formats and flexible output options
Cons of httpx
- Less focused on directory brute-forcing compared to dirsearch
- May require more setup and configuration for specific use cases
- Potentially overwhelming for users who only need simple directory enumeration
Code Comparison
httpx:
for result := range r.DNSClient.Enumerate(domain) {
    if result.Error != nil {
        gologger.Warning().Msgf("Could not enumerate DNS for %s: %s\n", domain, result.Error)
        continue
    }
    // Process result
}
dirsearch:
def scan(self):
    for path in self.dictionary:
        if not self.recursive and path.count("/") > self.currentDepth:
            continue
        url = self.base_path + path
        self.output.status_report(self.batch.count(), len(self.dictionary))
        self.batch.append(url)
Summary
httpx is a versatile tool for HTTP probing and analysis, offering broader functionality and faster performance. dirsearch specializes in directory enumeration with a focus on simplicity and ease of use. While httpx provides more features, dirsearch may be preferable for users specifically seeking directory brute-forcing capabilities.
Find domains and subdomains related to a given domain
Pros of assetfinder
- Focused on subdomain discovery, providing a specialized tool for this task
- Lightweight and fast, with minimal dependencies
- Supports multiple data sources for comprehensive subdomain enumeration
Cons of assetfinder
- Limited to subdomain discovery, lacking directory and file enumeration capabilities
- Does not support customizable wordlists or extensive configuration options
- May require additional tools for a complete web application reconnaissance
Code comparison
assetfinder:
func main() {
    domains := make(chan string)
    go func() {
        sc := bufio.NewScanner(os.Stdin)
        for sc.Scan() {
            domains <- sc.Text()
        }
        close(domains)
    }()
    // ... (processing logic)
}
dirsearch:
def main():
    parser = OptionParser(usage)
    for option in options:
        parser.add_option(option)
    options, arguments = parser.parse_args()
    # ... (configuration and execution logic)
The code snippets highlight the different approaches:
- assetfinder uses Go and focuses on efficient input processing
- dirsearch uses Python and emphasizes configuration options
Both tools serve different purposes in web application security testing, with assetfinder specializing in subdomain discovery and dirsearch excelling in directory and file enumeration.
Nuclei is a fast, customizable vulnerability scanner powered by the global security community and built on a simple YAML-based DSL, enabling collaboration to tackle trending vulnerabilities on the internet. It helps you find vulnerabilities in your applications, APIs, networks, DNS, and cloud configurations.
Pros of Nuclei
- More versatile, supporting various protocols and vulnerability types
- Highly customizable with YAML-based templates
- Active community and frequent updates
Cons of Nuclei
- Steeper learning curve due to its complexity
- Requires more setup and configuration compared to Dirsearch
Code Comparison
Dirsearch (Python):
def recursive_bruteforce(base_url, extensions, depth):
    if depth == 0:
        return
    for word in wordlist:
        for extension in extensions:
            url = f"{base_url}/{word}.{extension}"
            response = requests.get(url)
            if response.status_code == 200:
                print(f"Found: {url}")
                recursive_bruteforce(url, extensions, depth - 1)
Nuclei (Go):
func (r *Runner) runTemplates(ctx context.Context, target string) {
    for _, template := range r.options.Templates {
        if err := r.executeTemplate(ctx, template, target); err != nil {
            gologger.Warning().Msgf("Could not execute template %s: %s\n", template.ID, err)
        }
    }
}
The code snippets highlight the different approaches:
- Dirsearch focuses on directory and file enumeration
- Nuclei emphasizes template-based scanning for various vulnerabilities
Both tools are valuable for security testing, with Dirsearch being more specialized for directory discovery and Nuclei offering broader vulnerability scanning capabilities.
SecLists is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place. List types include usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and many more.
Pros of SecLists
- Comprehensive collection of multiple types of lists for security testing
- Regularly updated with community contributions
- Versatile for various security testing scenarios beyond web directory enumeration
Cons of SecLists
- Requires additional tools or scripts to utilize the lists effectively
- May contain outdated or irrelevant entries due to its extensive nature
- Not specifically optimized for web directory brute-forcing
Code Comparison
While a direct code comparison isn't applicable due to the nature of these projects, here's a brief example of how they might be used:
SecLists (used with a separate tool):
gobuster dir -u http://example.com -w /path/to/SecLists/Discovery/Web-Content/common.txt
dirsearch:
python3 dirsearch.py -u http://example.com -e php,html,js
SecLists provides raw data, while dirsearch is a complete tool with built-in functionality for web directory enumeration.
Convert  designs to code with AI
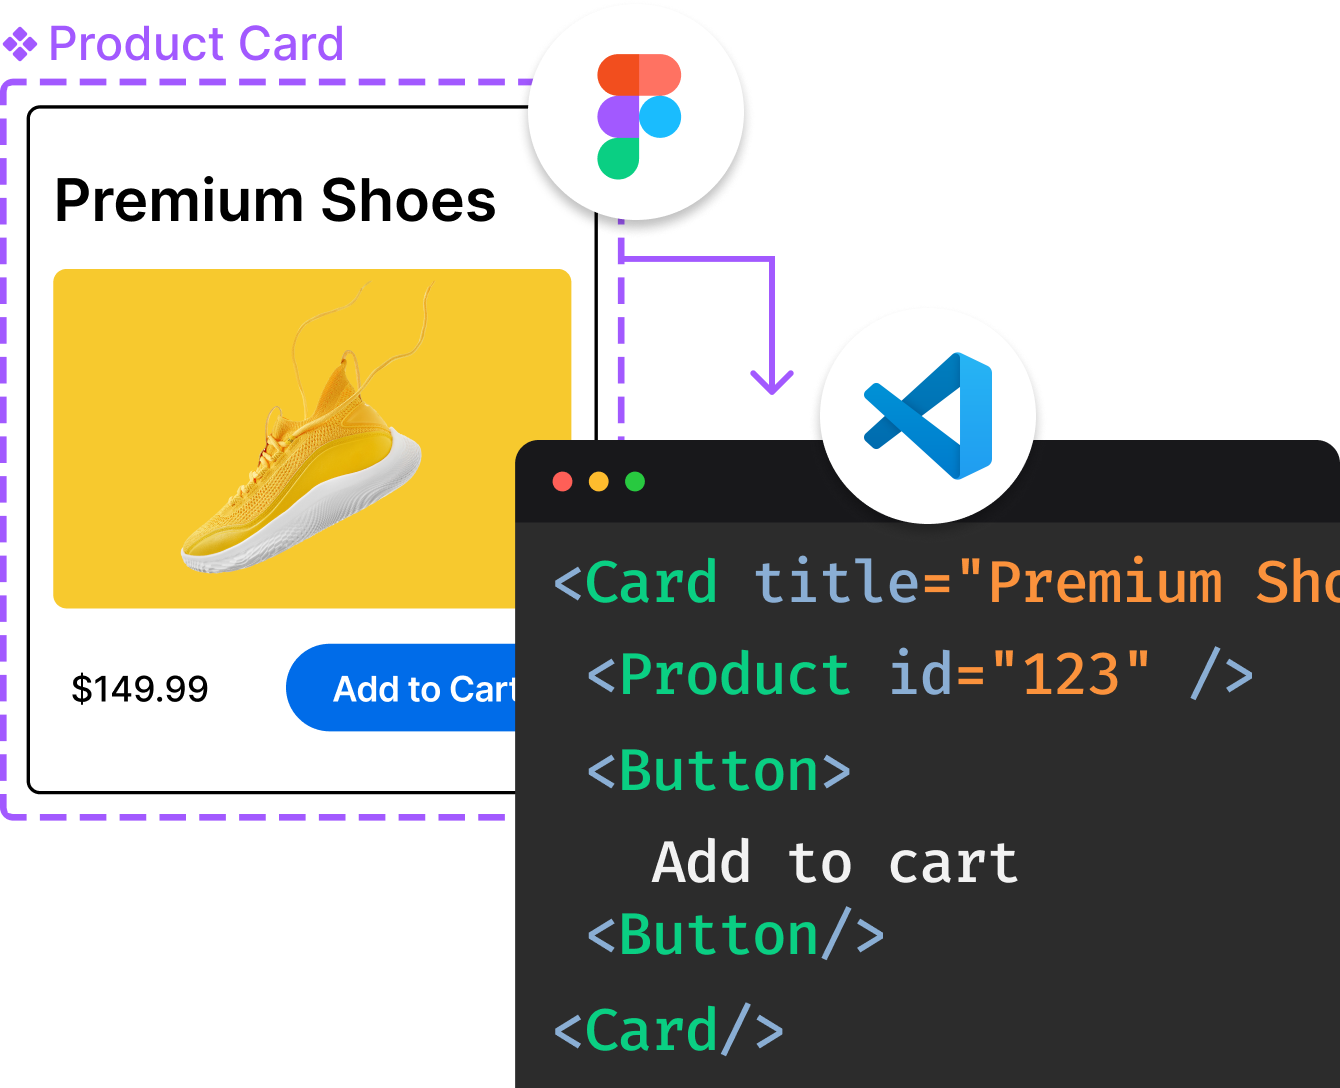
Introducing Visual Copilot: A new AI model to turn Figma designs to high quality code using your components.
Try Visual CopilotREADME


dirsearch - Web Path Discovery


An advanced web path brute-forcer
dirsearch is being actively developed by @maurosoria and @shelld3v.
Join the Discord server to communicate with the team.
Quick Start
dirsearch requires Python 3.11 or higher.
git clone https://github.com/maurosoria/dirsearch.git --depth 1
cd dirsearch
python3 dirsearch.py -u https://example.com -e php,html,js
You can also install the latest Python stack directly from GitHub with pip:
pip3 install git+https://github.com/maurosoria/dirsearch.git
dirsearch -u https://example.com -e php,html,js
The Rust native backend is opt-in for source installs; see Installation for the native build steps.
Pre-built PyInstaller binaries and portable folder archives are available on the Releases page.
Documentation
The full documentation now lives in docs/:
- Installation: supported platforms, Python install, release artifacts, and Docker.
- Usage Guide: common scans, recursion, filters, proxies, raw requests, reports, and tips.
- Wordlists:
%EXT%, categories, templates, prefixes, suffixes, and transformations. - CLI Options: complete command-line reference.
- Configuration:
config.inireference. - Sessions: save, list, and resume scan sessions.
- Python API: importable API examples.
- Building: PyInstaller, portable builds, Docker images, and GitHub Actions.
- References: external tutorials and articles.
Minimal Examples
python3 dirsearch.py -u https://target
python3 dirsearch.py -u https://target -e php,html,js
python3 dirsearch.py -u https://target -e php,html,js -w /path/to/wordlist
python3 dirsearch.py -u https://target -r --max-recursion-depth 3
Use python3 dirsearch.py -h for common options or python3 dirsearch.py -hh
for the complete CLI help.
Python API
dirsearch can also be used from Python code for local automation, MCP servers,
REST wrappers, and agent-controlled scans. The importable API keeps its
configuration in FuzzerConfig, so callers do not need to parse CLI flags or
mutate CLI globals.
See Python API for examples covering templates, custom wordlists, callbacks, authenticated sessions, and agent-oriented scan recipes.
Contributing
Pull requests and feature requests are welcome. See CONTRIBUTORS.md for the people who have helped improve dirsearch.
License
Copyright (C) Mauro Soria (maurosoria@gmail.com)
License: GNU General Public License, version 2.
Top Related Projects
Fast web fuzzer written in Go
Directory/File, DNS and VHost busting tool written in Go
httpx is a fast and multi-purpose HTTP toolkit that allows running multiple probes using the retryablehttp library.
Find domains and subdomains related to a given domain
Nuclei is a fast, customizable vulnerability scanner powered by the global security community and built on a simple YAML-based DSL, enabling collaboration to tackle trending vulnerabilities on the internet. It helps you find vulnerabilities in your applications, APIs, networks, DNS, and cloud configurations.
SecLists is the security tester's companion. It's a collection of multiple types of lists used during security assessments, collected in one place. List types include usernames, passwords, URLs, sensitive data patterns, fuzzing payloads, web shells, and many more.
Convert designs to code with AI
Introducing Visual Copilot: A new AI model to turn Figma designs to high quality code using your components.
Try Visual Copilot